External pressure
A customer, audit, insurer, or investor is asking questions the business can't answer with confidence.

Security advisor · fractional CISO
Fewer open questions reach your board, and your team gets a risk-ranked plan it can fund and execute.
Security is there to protect the business and enable revenue, which means finding a way to say yes to good work without slowing it down.
Built for small and mid-size US businesses and public-sector organizations that need senior security leadership before they can justify a full-time CISO.
Why the name
blackhole (networking) : a route that silently discards hostile traffic. Nothing malicious gets through, and nothing noisy gets out.
An engagement does the same thing. It absorbs the ambiguity, the vendor noise, and the half-finished findings, and hands leadership a short list of decisions worth making.
When to engage
Senior guidance earns its cost when the business needs a decision, an accountable owner, or a plan it can defend.
A customer, audit, insurer, or investor is asking questions the business can't answer with confidence.
Cloud, identity, application, or AI adoption is moving faster than anyone's mandate to govern it.
Work keeps piling up, and there's no risk-ranked order the team can fund and finish.
A raise, an enterprise deal, an audit, or a board meeting needs a credible security narrative before it lands.
Ways to engage
Each level spells out what I own, what your team keeps, and who it isn't for, so you can rule out two of them before we talk.
I'll go over pricing on the fit call once scope is clear. There are no packaged tiers, and you can leave any retainer.
Not sure? Take the 2-minute fit checkFocused engagements
Each one stands on its own or slots into a Sprint or a retained cadence.
AI governance
Acceptable-use policy, NIST AI RMF-based risk assessment, tool approval paths, and employee guidance, so adoption moves without exposing data.
Exercises
A facilitated exercise built around your actual systems, with an after-action report that gives every gap an owner.
Third-party risk
Every new tool is a new place your data lives. A repeatable review turns vendor risk into a documented decision procurement can act on.
Productivity suite
Identity, mail authentication, sharing, device, and admin settings reviewed against current baselines, with a sequenced hardening list.
Cloud
AWS and GCP (Azure on request): IAM, encryption, logging, and public exposure ranked by business impact and sequenced against engineering capacity.
Assurance
Guidance to audit or attestation readiness: control ownership, evidence operations, policy rollout, and auditor liaison. The audit itself is done by a separate firm you choose.
Each is scoped and priced on the fit call.
See all 12 focused engagementsApproach
Every engagement runs the same four steps in the same order, so you always know which one we're in.
Your business, your obligations, and what a good outcome looks like to leadership.
Controls, gaps, and exposure, measured against the decisions you actually face. The evidence comes from interviews, documentation, and a read-only review of what you choose to show, with tooling only when the scope calls for it.
A short, funded sequence that also names what we're deliberately not doing.
Review, coaching, vendor coordination, and reporting that keep the plan moving.
"Most growing companies can wait on a full-time security hire if someone senior gives them a roadmap they can carry out without slowing down."
What you hold at day 30
Every engagement produces these, starting in its first month. They're yours to reuse and to hand to whoever comes next.
DOC 01
Where you are, where the business needs you to be, and the gap in between.
DOC 02
Each risk tied to exposure, urgency, a named owner, and a decision path.
DOC 03
Options and tradeoffs a board can read in ten minutes and act on.
DOC 04
Sequenced against real capacity, with accountable next steps.
The advisor
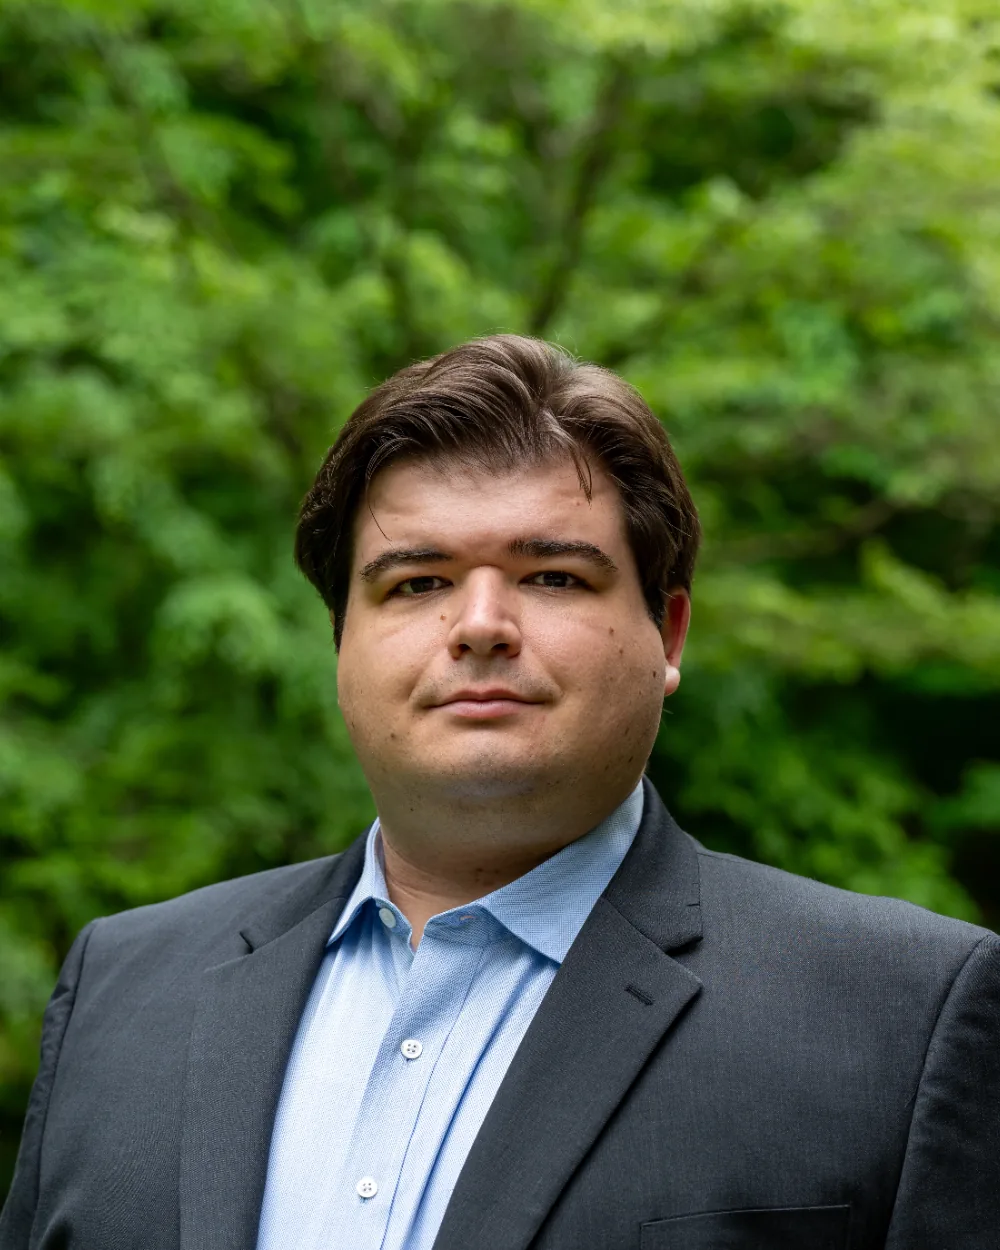
Alex Sellers CISSP, CISM
I'm Alex Sellers, and I lead Blackhole Cyberstrategy. I work on strategy, governance, risk prioritization, and security programs leaders can understand and sustain. That covers AI governance, SOC 2 and ISO readiness, application and cloud security, vulnerability reduction, tabletop exercises, and executive security planning.
When the scope calls for it, vetted senior practitioners join the engagement under the same terms, and I stay your point of contact.
Next step
Bring the security decision or business milestone you're preparing for. You'll leave with a straight answer about whether it's worth continuing, even if that answer is no.
Please don't send credentials, logs, reports, diagrams, or incident evidence at this stage, and never by email.
What happens
Or email hello@blackholecyberstrategy.com